Notes /
Check the quiet web app's logs
Even a tiny shop attracts bot probes. Reviewing the 404s made it easier to see the noise and tighten the WAF rules.
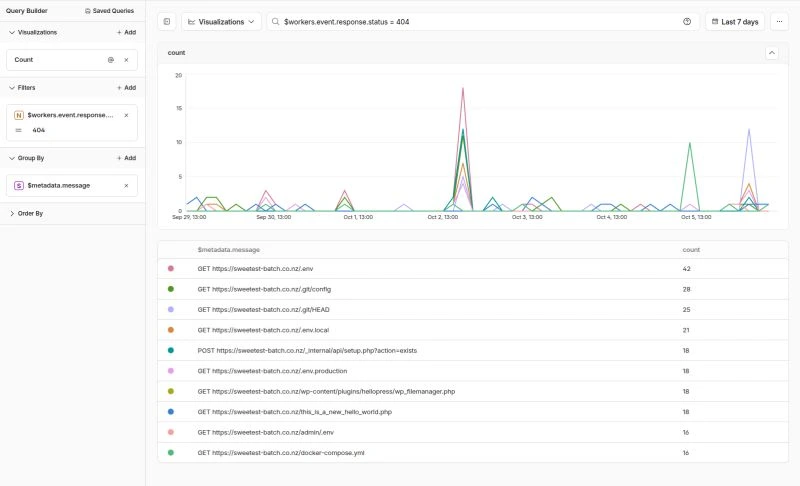
Friendly reminder: check your web app logs periodically.
Last week I looked at the logs for a tiny online shop. The 404s were dominated by bots looking for paths such as /.env, /.git/config and WordPress PHP files. The screenshot shows the pattern: repeated probes for files and endpoints the application doesn’t serve.
I’d already blocked many probes before they reached the Worker, but the traffic still made the wider analytics noisy. The requests that did reach the application were a useful reminder to review the rules again.
I tightened the WAF rules. A small app can be quiet on the customer side and busy with automated probes at the same time.
Go have a look at yours.
Also posted on LinkedIn ↗